
ルールを学べ:ハッカーの思考法
Learn the rules: The hacker mindset
ルールを学べ:ハッカーの思考法
Microsoft Research Podcast
要約
Microsoft Research のリサーチマネージャー Mike Walker が、少年時代から DARPA の Cyber Grand Challenge、現在の AI とセキュリティ研究までの歩みを語った回。ルールは社会的な構築物であり、ユーザーの信頼を損なうとセキュリティは成り立たないという考えや、攻撃と防御は同じスキルセットだという見方を示した。マウンテンバイクや、チームの社会的知性、リーダーシップに関する教訓にも話が及ぶ。
この回のポイント
- ●Walker は、ルールを理解してこそ望むことができるとしつつ、ルールは社会的な構築物であり、セキュリティがユーザーに何かを求めるたびに貴重な「信頼」を消費すると述べている。
- ●DARPA の Cyber Grand Challenge(CGC)は、人間の Capture the Flag を機械同士で行う初の完全自律ハッキング大会で、エアギャップ環境で実施された。当時は機械学習ではなくエキスパートシステムの競技だったという。
- ●当時のエキスパートシステム的な技術基盤は、現在ではモデルを動かす「ハーネス」として使われていると指摘し、AIxCC の Team Atlanta による MDASH を例に挙げた。
- ●レッド/ブルー/パープルチームの区別は単純化にすぎず、暗号ツールとランサムウェアのように、セキュリティ技術の多くは鍵を誰が握るかで攻防が変わる二重用途だと説明した。
- ●Project FRETA は、改ざん対策としてソフトウェアではなくクラウドのハードウェアからメモリ情報を取得し、全システムのメモリ解析を行う取り組みだと紹介された。
- ●意思決定への批判に対して「自分が知らない情報があるのでは」と問う姿勢や、技術チームのEQ・社会的知性の重要性が、本人の教訓として語られた。
章立て
少年時代とハッカー気質の原点
オハイオとバージニアの農場で育ち、父が持ち帰る産業機器や Apple II、BBS に触れた経験を語る。後にそれがキャリアにつながった。
ルールは社会的な構築物
ルールへの関心と、セキュリティが求める信頼の価値を語る。思考実験「No Vehicles in the Park」にも触れる。
9.11 後の人材探しと CTF
9.11 後にセキュリティ人材の需要が高まり、DEF CON の Capture the Flag に参加するようになった経緯と、その競技の仕組みを説明する。
Cyber Grand Challenge と AI の変化
機械同士のハッキング大会 CGC の内容と、現在のモデル中心の時代との違い、攻撃コスト構造の変化を論じる。
攻防は同じスキル:パープルチームと FRETA
攻撃と防御が二重用途の技術であることを説明し、改ざん対策としてクラウドハードウェアからメモリを取得する Project FRETA を紹介する。
自転車と Orange Crush
膝の怪我から始まったマウンテンバイク、100マイルレースの準備、自作のグラベルバイクについて語る。
ライトニングラウンドと教訓
リーダーシップに関する助言、チームの社会的知性という教訓、ジャグリングやSF作家への憧れなどを語る。
解説記事
Microsoft Research Podcast の今回のゲストは、AI・サイバーセキュリティ・大規模分散システムの交差点で研究を率いる Mike Walker。DARPA で Cyber Grand Challenge(CGC)を主導した経歴を持つ。聞き手の Weisheng Liu が、少年時代から現在までの歩みと、ハッカー的な思考の核心を尋ねた。
ルールは社会的な構築物
Walker は少年時代、科学者でありベンチャーキャピタリストでもある父が持ち帰る産業機器を渡され、「これで何か作ってみろ」と言われて育った。Apple II やダイヤルアップの BBS にも夢中になり、後になってそれが職業として「名前を持った」と振り返っている。
印象的なのはルールをめぐる発言だ。ルールを理解しなければやりたいことはできない、と述べたうえで、ルールは社会的な構築物だと強調する。セキュリティの仕組みがユーザーに何かを求めるたびに、それは「信頼」を消費している。信頼を浪費すればセキュリティ体制は崩れる、という見方だ。そのため、ルールを機械的に即断するのではなく、社会的文脈を理解することが重要だと述べている。
CTF から Cyber Grand Challenge へ
9.11 の当日、Walker は通信系スタートアップで働いており、その後ワシントン周辺でセキュリティ人材の探索が始まったと語る。その流れで DEF CON の Capture the Flag に関わるようになった。CTF は、主催者がその場で初めて渡す未知のソフトウェアを、各チームが解析して守りつつ、他チームから「フラグ」を奪う競技だと説明された。
DARPA の担当者たちは「人間のサッカーに対するロボットサッカー」を発想し、機械同士が戦う大会を構想した。それが CGC である。完全自律システムがエアギャップ環境で攻防を行い、失敗しても人が再起動することはできない。各チームは数年かけてシステムを作ったが、敵対する機械との初対決に事前に備える方法は乏しく、結果を見守るしかなかったという。
Walker は、当時の CGC は機械学習ではなくエキスパートシステム(専門知識を規則化した従来型システム)の競技だったと位置づける。一方で、その技術基盤は今日、モデルを動かす「ハーネス」として使われているとも述べた。例として、AIxCC で優勝した Team Atlanta のメンバーが開発する MDASH を挙げ、モデルで動くサイバー推論システムと呼べるものだと紹介している。
攻撃と防御は同じスキルセット
現在のセキュリティについて Walker は、これまでのネットワーク社会の均衡は「攻撃能力の希少性」によって保たれていたが、そのコスト構造がモデルの能力によって覆されつつあるという認識を示した。
レッドチーム/ブルーチームの区別についても、攻撃者と防御者の人為的な分離にすぎないと述べる。ファイルを暗号化するプログラムは、鍵を誰が持つかで暗号ユーティリティにもランサムウェアにもなる。遠隔操作ツールも同様だ。つまりセキュリティ技術は本質的に二重用途であり、パープルチームはその事実を認めた考え方だという。攻撃者も侵入後は発覚しないよう自らを守り、防御者も脆弱性を見つけて評価するにはエクスプロイトという攻撃的手法を使う。両者は同じ道具と技能を共有している。
彼のチーム(New Security Ventures)は「攻撃を意識した防御ツール」を開発している。紹介された Project FRETA は、改ざん(tampering)への対策がテーマだ。防犯カメラの映像を偽物にすり替える例えを使い、攻撃者にとって改ざんは見つからずに侵入する容易な手段だと説明する。FRETA は、取り外しや改ざんが可能なソフトウェアではなく、クラウドのハードウェアからメモリ信号を取得し、全システムのメモリ解析環境を一から構築する試みだという。技術を公開することと、その展開方法を明かすことは別だとも述べ、攻防のゲーム理論的な側面をポーカーの駆け引きにたとえた。
教訓:知らない情報と社会的知性
後半はパーソナルな話題が中心だ。膝の怪我をきっかけに始めたマウンテンバイクでは、100マイルのレース High Cascades 100 で 329 人中 69 位に入ったと紹介された。トレーニングプランに忠実すぎて「トレーナーロボット」になるなと助言された、という逸話も語られた。
ライトニングラウンドでは、二つの教訓が目を引く。一つは、メンターから「納得できない決定は、あなたが持たない情報の結果ではないか」と問われた経験だ。以来、決定を聞くたびに「相手は何を知っているのか」と考える姿勢が習慣になったという。もう一つは、CTF の予選で、すでに解かれた問題に取り組む仲間がいると気づいた経験だ。チームの IQ は測れても、連携の度合いは測れない。ヒーロー個人に頼るのではなく、技術チームに社会的知性(EQ)を築く方法を考えるようになったと語っている。
まとめ
本エピソードは、セキュリティを「禁止事項の集合」ではなく、信頼と社会的文脈の上に成り立つ営みとして捉える視点を示している。日本の読者にとって注目すべき点は三つある。第一に、攻撃と防御は同一の技術基盤を共有するという見方で、AI を防御に使う際にもツール自体が標的になる前提が必要になる。第二に、CGC で培われた自動化の技術がモデル時代にはハーネスとして再利用されているという指摘。第三に、チームの連携や意思決定の透明性といった、技術以外の要素が成果を左右するという教訓である。ハッカー的な好奇心と、ルールや人への洞察を両立させる姿勢が、全体を通じて語られていた。
文字起こし(英語・自動生成)
Well, you have to understand the rules if you want to be able to do what you want. So I have a definite fascination with the rules. But the thing you have to understand about the rules is that rules are a social construct. And I think that a lot of, in the computer security field, when people hear the word security and they think about the rules that the security system is imposing on them, And every time a security system asks something of users, then you're asking for their trust, and that trust is a precious commodity. And so when you squander user trust, then the security regime falls down. So I think it's really important to understand the social context of rules instead of just having instant adjudication. This is the Microsoft Research Podcast. where Microsoft researchers,
driving advancement through fundamental science and technology research, explore the who, how, and what's next in computing and AI. Hi, and welcome. My name is Weisheng Liu, and I'm a Principal Technical Program Manager here at Microsoft Research. And today, I'm joined by Mike Walker, who's a Research Manager here in MSR, Microsoft Research, where he leads projects at the intersection of AI, cybersecurity, and large distributed systems. Before Microsoft, Mike led DARPA's Cyber Grand Challenge, the pioneering program that demonstrated autonomous AI systems capable of finding and patching software vulnerabilities. And CGC actually just celebrated its 10th anniversary this year in 2026. Mike's work spans groundbreaking efforts that include cloud-native memory analysis, automated malware analysis, and next-generation cyber defense technologies. Mike, thanks for joining me. Good to be here, Wes. All right. So, Mike, we have known each other for a couple of years now, and I've heard like bits and pieces of your story over time as we've gotten to talk.
But before I really knew who you were sort of as a person, I kind of knew you were like Mike Walker, the hacker guy that's working over there, which I'm sure you love. And I know you love that when I call you the hacker. But you've worked on so many things that I've never really thought about before. and, like, new words have entered my vocabulary as a result of knowing you and working with you, like threat intelligence, nation states. And I think there are a couple other words that I think would have never been in my lexicon had I not known you. So I'm hoping we can spend this time to also have the audience get to know you as well. So we're going to start at the beginning then. And the beginning is, I believe, Mike, you grew up in Ohio? Columbus, Ohio. Columbus, Ohio. What kind of kid were you in Columbus, Ohio? I think I was a kid who spent a lot of time in the woods. I was a skateboard kid. I was a basketball kid. But I think mostly I was a kid who read books and lived in a world of their own imagination.
Were you on a farm in Columbus, Ohio? Or were you in like, or is this more suburban, rural, urban? It was halves and halves. I spent most of the year in Columbus, Ohio, and then every summer I would go out to the town of Tappahannock on the Rappahannock River in Virginia, and I lived completely on the farm. So what was the lifestyle and what you were doing different between Columbus, Ohio and the farm? Um, so like some things that I was doing in Columbus, Ohio is that, um, my father who was sort of half scientist, half venture capitalist, um, would bring me home industrial equipment and say, see what you can make out of this and drop it in my room. Really dangerous stuff. Uh, and, and, uh, he would always give me safety warnings, right? Like, uh, this is a helium neon laser. You know, this is, uh, this tube is made out of glass. Don't break it. and then this is a really, really high voltage power supply driving it and it can arc and kill you, right?
And I knew what that meant. And then he would leave me with it. What can you make out of this? So I would do stuff like try to replicate the Michelson-Morley experiment because I had the table and the mirrors and I could do that. And then also I spent a lot of time with the Apple II, which was this just incredible machine from some other universe that I had never gone to. I later found out that was, you know, hackerspace and information technology culture. But it came from nowhere, and there was nobody I could talk to about it. And so I spent a lot of time trying to hook the Apple II up to stuff in my life and try to control it with that thing. Okay, so you brought up some hacker stuff. So I have to ask, there was farm stuff, there was, you know, dad brought home interesting tools and equipment. How did all of that get you interested in cybersecurity? I think I was always in cybersecurity.
I just didn't know. Explain. You know, there's this idea that you live two lives, the one before you find out your purpose and the one after you find it. this was sort of life before purpose where I didn't know why I was so interested in how these things worked. So, you know, I ran a bulletin board system before the internet. This was how computers communicated with each other, dial up modems, not even backbone linked. Each BBS bulletin board system was a universe unto itself, you know, architected by its creator. And so there or all these little universes you could dial into. And then at some point, all these things I'd been doing my whole life sort of got connected to a career. When you say, you know, somebody could, right, somebody could listen to every single badge swipe event on the network on campus
and then replicate them and badge themselves into any building they wanted because this is all in a broadcast land. and somebody should change that. There was a time when if you said things like that, the people you told it to would just be like, well, don't do that. Did you listen to them? No. I would joke. And then at some point, the world started getting serious about imposing rules onto network computers and they started hiring people who were interested in that. And suddenly it was a career, right? Oh, I was always here, but now it has a name. So I have to ask, you brought up the notion of rules. I feel like cybersecurity and rules has a relationship there. How much of a rule follower were you growing up versus how much do you think you are a rule follower now?
And was there a difference, or have you always been some version of rule following? Well, you have to understand the rules if you want to be able to do what you want. Yes. So I have a definite fascination with the rules. But the thing you have to understand about the rules is that rules are a social construct. And I think that a lot of, in the computer security field, when people hear the word security and they think about the rules that the security system is imposing on them, every time a security system asks something of users, then you're asking for their trust, and that trust is a precious commodity. And so when you squander user trust, then the security regime falls down. So I think it's really important to understand the social context of rules
instead of just having instant adjudication. Okay. I am going to have to ask you then about a game that we played recently called No Vehicles in the Park. No Vehicles in the Park is a game about content moderation is one way to look at it. I think it's a fascinating thought experiment. But it just takes the thesis that rules are simple and challenges it with putting the player in the position of judge. And so the name of the exercise is the name of the rule, which is no vehicles in the park. And then it asks you some very simple common sense questions about is this a violation of the rule, no vehicles in the park. Like if the International Space Station overflies the park, is that a vehicle in the park and is it against the rules? Mike, do you think the ISS flying over the park is a violation of the rules?
No. But it's important that we have a resilient way to adjudicate things that bridges social norms. Okay. How much did you agree with the population, by the way, that's no vehicles in the park? I've rarely ever broken 50%. I play often. I think I got 96% on my first try. So I think I, does that mean I'm kind of like a lemming that just understands the social construct of rules? I think it means you channel the zeitgeist. Okay. I've been assimilated. That's what it feels like. All right. So let's talk about something that I love, which is you had a short segment in 60 Minutes where you had a conversation with Leslie Stahl. and she described you as one of the world's top hackers,
at least at the time in which she interviewed you. And so now I have to know, how did you find hacker cultures? What was the extent of your involvement? And, Lena, how did you really get into it? It sort of happened all at once. And I can tell the beginning of the story, and then I can tell you the day that the story stops. Um, so the, the beginning of the story is that I was working at a, at a startup building telecommunications technologies, um, on September 11th, 2001. And I was living in, um, Maryland, uh, outside of Washington DC, but my wife was in Washington DC on that day. And then all the phones stopped working. My workplace was overflowing by an F-16. And after that in the nation capital there was this sudden talent search for people who understood computer security or people who always been there but didn know what it was called
And that talent search found me. What were the qualifications that you had that matched with their list of talent that they were looking for? I wish I knew. World's top hacker? I think that that label was placed on me much later. I think that I became part of a series of cultures after that day, and one of them was the group of people who play in DEF CON Capture the Flag, which is a hacking contest in Las Vegas. and when you start getting involved in trying to get get better at something in a way where you can compete at a national or international level especially in sort of a coffee house environment where everyone else is trying to get better too it sort of propels you upward very quickly. Okay let's let's go back later to talk about capture the flag because I think it's it's related
to the sort of next arc of your life, which was your time as a project manager, program manager at the Defense Advanced Research Projects Agency, also known as DARPA, which is also why Leslie had been interviewing you at the time. It was associated with your affiliation at DARPA. And you were there for about four years. How did you go from, you know, let's say, call to action from the nation's capital, looking for people with your specific set of skills to being at DARPA as a PM. So we should be clear. We've just sort of skipped over 11 years of Mike trying to get better at hacking. You were world's top. Look, I just believe world's top hacker, one of the world's top hackers. Well, I think my friends, colleagues, and teammates from the time, if they were here to hear that accusation being made, would give me endless grief about it.
Certainly, there was sort of a golden age of capture the flag, and I got to be part of it and see some of the people. I got to see the game change over time. But it was a competition, and it was very reflective of a skill set that was of national interest. I think at the same time, the think tank Rand had published an opinion piece called Hackers Wanted, which sort of described the immense need for more people who could think that way at a high level. And DARPA, specifically Norm Whitaker and Dan Kaufman, who were leading I2O. DARPA Dan. DARPA Dan. Looked at the game of hackers, right? And if you could think of that as soccer, their immediate question was, what about robot soccer? You know, could we make automated systems that could play this game? And so they encountered myself and some colleagues giving a talk about sort of the interleaving of Capture the Flag as, you know, hacking contests and talent development.
And they said, you know, could you do talent development for computers the same way, right? Could machines play Capture the Flag? And that was the beginning of the conversation about building the world's first all-machine hacking tournament. Okay, so now maybe let's go back and explain what DEF CON, Capture the Flag was, or CTS, because I think a lot of us who are, again, not in the space, you say Capture the Flag, and I'm thinking like summer camp, and, you know, there are two teams, and there's kids who hide flags, and then you try to run around and find the flag. You find the defenders and whatnot. So what was the DEF CON version of this? It's changed over time. That's the thing about this game that I should lead with is that Capture the Flag is different with every generation. And at least in my opinion, I think it's gotten better with every generation, right? Each hacking group that's picked up the lessons of the past in the game has made it better. But it is sort of based around that playground idea, right? My team has some flags.
Your team has some flags. We're going to try to take each other's flags. Whoever takes the most wins, right? It is that simple. Now, there are more than two teams, somewhere between 8 and 16, and each team is trying to take flags from every other team. They're trying to protect their own flags. But, of course, the flags are made of data, right, or control over a network system. And the way that you protect your own data and control of your own network system is network defense, right, and computer defense, and the way that you take flags from other teams is you hack into their servers. And you take their flags, and you do it without getting caught. And then what makes this game sort of unique is that all the software that you're protecting is written just for that game. It will never be used again. It's boutique. It was written by the organizers, kept in secret, revealed to the teams the minute they sit down.
They've got new software they've never seen before. They don't know what it does. and they're in a race to understand it and they're racing everybody else. Because if you can understand it, then you can protect it. And if you can understand it, you can hack it. Okay, so let's get into this thing called DARPA's Cyber Grand Challenge, or CGC, which just celebrated its 10th anniversary. And so from what I understand, CTS, humans playing soccer, CGC, robots playing soccer? Is that probably a good way to... That's exactly it. Okay. So now explain to me a little bit further, like, what was CGC? What was your role? And then more importantly, did it feel historic at the time or just kind of impossible and you somehow figured out with a large group of folks at DARPA, this is how we're going to solve this impossible thing? Well, there's two ways to answer that. There's the day before it worked and the day after it worked. Right. There were actually three and a half years before it worked.
So if you'd asked me, I think in any of that three and a half years, I would have said, let's wait and see. So what was it, though? By the way, I think you can watch the first CGC online. There's a whole recording of the event. There's a recording of the event, which we had sportscasted live with announcers. And so you can watch it as it happened. And it was a capture the flag, right, protect data, steal data, that was run entirely by autonomous systems behind an air gap. So if they failed, there was no person even to turn them off and turn them back on again. So how did, so if I think about how you just described capture the flag with DEF CON, But there were, like, people on the floor coding. I'm assuming, though, you're saying CGC did not have that.
So were there teams that had, like, pre-created something? Yes, they spent many years of their life, actually, building these autonomous systems. And you can't really pre-flight an autonomous system whose purpose is to fight. You can pre-flight an autonomous system whose purpose is to maybe go for a drive, right? You can take it for a drive. But if you're going to fight other systems, you have to, like, build another one, right? And we did give them some exposure to a sort of scripted opponent. The DARPA infrastructure team built a scripted opponent and attempted to give teams some pre-exposure. But that first confrontation between adversarial hacking machines, there wasn't really a great way to prepare for it. And so the teams were in this really tough position of watching the systems play, win, or lose in a way where they couldn't do anything but watch.
So, you know, I want you to think back on that time as well, because, like, now when we're talking about AI, it seems a little bit more commonplace, right? We're like, oh, you know, we have GPT, we have CLOD, we have a lot of other models as well. So, like, how historic was that? Because I think it can't be understated how vastly different sort of autonomous artificial intelligence capabilities were like 10 years ago versus now. It was a different universe of capability. And Cyber Grand Challenge had a role in the development of the technology stacks that we're seeing today, but it was an expert systems contest. There was no, at that time, we would have called it machine learning, but there's no real involvement, critical involvement in machine learning. But there was this fusion of tooling where you had sort of an autonomous set of tools that could perform a lot of these tasks as far as conventional compute could push the state of the practice at the time.
I think if we look back from the perspective of today, which is still a perspective that's difficult to keep up with and difficult to appreciate how radically different the intelligence displayed by today's models is from what we had in 2013, 2016, we're still seeing the technology stacks that we would have called expert systems in 2016 being used as what we call a harness today so if just to talk about another DARPA project AIXCC which happened a few years ago some of the people from Team Atlanta which won that competition are building a harness called MDASH, which is, I think we could call it a cyber reasoning system that is powered by models and used to do these sorts of tasks autonomously.
You were interviewed by the New York Times in 2016 about CGC, and you said that making network technology safer was a challenge for civilization. And, you know, what do you think about that? Has civilization made progress on you know resolving that challenge And what are some tangible takeaways that you think from 10 years ago until now think through about how we making things safer for civilization? I'd say that's as true now as it was then, maybe more so. And I think our dependence on network systems for every piece of civilization has only increased. I think it's difficult to buy a car or to participate in a utility grid that isn't networked. Right. How we're doing, I think that we're seeing a great disruption of the status quo right now.
I think that we reached a pretty steady state equilibrium where our security in our network civilization was sort of dictated by offensive scarcity. There was a known cost for high-end computer network attack. And that cost equation has been completely upended by the capabilities of models. So in thinking about sort of capabilities and models then, some terms that I've heard used are things when we're testing models, for example, as we call it, red teaming. But then I also hear that there's something called blue teaming. And then, of course, if you've taken primary colors or understood kindergarten primary colors, if you put red and blue together, you get purple teaming. Can you explain to the audience a little bit about those differences? Yeah. Red team and blue team is sort of an artificial separation between being an attacker and being a defender.
And it's also sort of an oversimplification and an abnegation of capability, right? Attackers attack, defenders defend. but if you take that simplification away and you look at what's going on under the hood, you'll see that the difference between offense and defense most of the time is sort of who's in control or who's driving. If you were to give a name to a program that encrypted every file on your computer and then unlocked it when you needed it, that is either a cryptography utility or it's ransomware depending on who holds the key. If you were to give a name to a program that allows you to log into your computer remotely and control it, maybe your home automation setup, that is either malware or a remote administration utility
depending on who holds the key, right, who holds the key. So there's this sort of blurring of offense and defense where computer security capabilities at their most atomic, basic level aren't offensive or defensive. They're dual use. And so the idea of red teaming and blue teaming is sort of this idea that we can impose single use onto dual use capabilities. And purple team is the acknowledgement that that's not true, right? Attackers, as soon as they break into a network, they have an intrusion that they need to defend. You'll hear all these terms like moving laterally, which just means breaking into more computers, or exfiltration, which means taking data. But the whole time they're doing that, they're trying not to get caught, right? So they're defending their attack, right? And at the same time, when defenders are doing things like log analysis or traffic analysis, their tools themselves can be broken into.
They have a duty to defend their own tooling. and they also need to, in order to prevent attackers, they need to be able to find vulnerabilities, find weaknesses, and then grade weaknesses in their own software. And the way that you find vulnerabilities is vulnerability research and you grade weaknesses by writing exploits or at least proof of vulnerability, and that's offense, right? So Purple Team is just this idea that attack and defense are the same skill set, They're the same tooling. They're blended. And it's really a contest to control the logic and memory of networked computers run all the time. All right. So I'm going to ask you a little bit about the team that you manage. Then it's called New Security Ventures. And would you classify the type of work that you and your team do as being red, blue, or purple? Or are we going to introduce a different color from the rainbow? I think that we do highly offense-aware defensive tool development.
So we build defensive tools, but we build them knowing that they are a target. What's one example of a project that your team has been working on? We have a project we call Project FRETA. It's named after the birthplace of Mary Curie, the pioneer of battlefield imaging. and the idea is that well first I actually need to introduce tampering we think of ourselves as the solution to tampering but first what's tampering what problem are we solving so let's say that my job is to break into a store undiscovered it's mission impossible I'm going to break in take the Doritos not get caught hold on what flavor of Doritos? I don't know What? I don't know. I don't actually eat them. I'm sorry. Okay, fine. But that's, you know, it's mission impossible. I have to take them. You've got to go get Doritos. I have to show up on the video. I can compute this path of not being observed by the video camera.
It's really hard, right? Maybe I do some kung fu, some gymnastics. I slide into the laser wire. I grab it, and I get out. But there is another way to break in and not get caught, which is to walk in, right, wave at the camera. cut the feed on the camera, take it down, replace it with a fake video camera that just plays good video like there's nobody in the store, and then go in and change the tape and leave. That's tampering, right? Yeah. And it sounds actually less complicated, right, than trying to simply not be observed. And if you look in the computer security world at tampering, tampering is often the easier way to accomplish the objective of an attacker, which is to break in and not get caught. and defend their intrusion, right? They're doing defense while they're doing offense. And so Project Frate is an attempt to solve that at cloud scale, to make it so that when defenders acquire defensive signals, right,
telemetry signals about what's happening in computers, they don't do it with software that can be removed or tampered with. They do it by acquiring signals from cloud hardware. And so we're a whole system memory analysis environment built from the ground up for looking at memory that's acquired from cloud hardware. So, okay, so you just revealed, for example, how Project Fretto works and how it protects or is trying to defend against something like Tamper. But then, you know, I'm kind of curious, though, you just revealed how it works. So, you know, you're kind of telling the attackers what you're doing and how you're defending. How does that work? If you're like, this is how I'm defending my castle, here you go. Well, you can reveal a technology or you can reveal its deployment. And I've revealed a technology and I haven't said anything about its deployment. Okay.
So there's a difference and there's layers that you've described so that, you know, even though you've revealed something, you haven't revealed the full extent. Well, you're bringing up a really interesting part of the game theory of adversarial computer network attack, computer network defense, which is that attackers condition their behavior based on their perception of what the defense is doing. And so that gets into these strange effects of, is the best way to protect a network to say that you have something or to actually have it, or to have a mismatch between what you say you have and what you have. So you're like bluffing in poker? There's a reason this game is played in Vegas. Okay. Okay. So we've had some more serious topics for a while, Well, and I want to get into something that maybe a lot of folks who maybe even know you don't know about you,
which is you love, I think I'm going to use, I think I can say love, cycling. That's true. How did you get into cycling? I got into cycling in sort of the way that I've gotten into a lot of things in my life, which is I got into it through what I thought at the time was a disaster. I blew out my knee playing basketball, which was one of my first great loves, right? And I went through surgical repair. And afterwards, the surgeon told me, you can't do the stuff with this knee that you used to do. And I was like, well, what can I do? You know, I hadn't even thought to ask this question before surgery. I'm sitting there trying to, like, rehabilitate the knee. And he said, well, you could try swimming or you could try riding a bike. I didn't really know anything about year one. You know, I used to ride a bike to get around. And then a friend of mine in college introduced me to mountain biking, which is sort of this idea that you could take a bicycle, which is a very stable system.
You know, you go out, you ride it down the sidewalk, it works great, and ride it over, you know, just horrible, you know, really steep, but rough terrain that no one should ever try to ride a bike on. Okay, and you did this recently at a 100-mile endurance race called High Cascades. High Cascades 100. And what was it like to prep for that? Because I feel like you've been working on some very important things on the professional side, and then you also had this big 100-mile endurance race that you were prepping for on the personal side. how'd that go there are very few things in life where you have a uh a fixed date in time where you have to show up and deal with uncertainty and uh uh ultra endurance racing is one of those um there's there's the parts that you can prepare for and the parts you can't right you can't prepare for the smoke forecast or the weather um you can just have a range of options but then you know as far as the conditioning i do spend a lot of time on the indoor trainer i just wake up really early I have a whole structured plan I think I started around January to race in July Do you follow them like you follow rules
Well, I'm much more strict about following my training plan. Actually, I think I've been advised, this is real, not to be trainer robot. Wow. So I had to back off on being trainer robot. Okay, so you had to ease up on the rules that you were following, that you wrote for yourself. Yeah, there's this mode. All the cycling fans watching this are going to be like, oh, my gosh, it's taking a buck. There's this mode called Erg Mode where the trainer decides how hard you should pedal. And so I would just set it to that and do what it told me. And so it was this big thing to actually go into free ride and try to ride the terrain. But, yeah, back off and try to listen to your body a little bit rather than just do whatever it takes. I feel like there's a relationship between what we're talking about now and something maybe related to the cybersecurity side of Mike.
but I have to I really want to get a photo of this on this podcast this video podcast so I am going to ask you about Orange Crush can you tell the audience what is Orange Crush? Orange Crush is the project bike that I built over the year where I was out with a blown shoulder I think that's when I met you yeah the problem with riding the bikes down the steep hills It's like sometimes it doesn't go completely perfect. We also had a colleague who also likes to mountain bike who broke his back around the same time you had a shoulder injury. Also mountain biking. Yeah, kind of depends on how you break your back versus how you break your shoulder and which one of those works out better. I messed my shoulder up pretty good, so it took some time. But it meant that I got to kind of conceive of something and put it together, They're mostly left-handed, which is its own challenge.
So it's a gravel bike, and, of course, my wife named it. She gets the naming rights because she's better at it. But it is very orange. We're coming up close on time, so I'm going to start wrapping up with a few questions. But I love this question, and I can't help but ask you, Mike, What is the difference between suffering on a bike and suffering through a hard technical project? I don't think of riding a bike suffering at all. That's like the good part. Even, okay, because in your 100-mile endurance race on High Cascades, I think you said it was like nine hours of nonstop riding, like in terrain. Racing, yeah. That seems like there might have been a little bit of suffering. No, that's absolutely the best part. No, no. The suffering is the checklist and the logistics the day before. Suffering is going out for a pre-ride and getting a flat and trying to find a bike shop that can get a tire patch in the day before High Cascades.
No, the logistics and the worrying, right, that's always the hard part. Once you're out, you know, it just gets worse and worse up until the start, and then you're racing and it's wonderful. and I want the audience to know, because High Cascades, you can actually look it up on the Internet. That's true. Mike finished 69th out of 329 participants. That's pretty darn good. I don't even know how to ride a bike, Mike. I race these days to learn about myself. Do you work on hard technical projects to also learn about yourself? I work on hard technical projects half because just getting to solve hacking problems is sort of what I've always done. But then also I get to work with great people, and I get to see impact. I get to see the impact of our work.
All right. So I have a lightning round of questions that I'm going to ask you. So just come up with, it's not a Rorschach test. Just come up with like. It might be. It requires pictures if I did it. But we're going to do a lightning round. So the first one, advice that blew your mind or change your perspective. I remember when I was starting at the agency. um i was i'd i'd worked in an engineering shop for a long time and the culture of many engineering shops is to be critical of leadership right they would see what leadership did and then uh take the information they had and be critical of the decision not all the time but sometimes. And, um, I had a mentor who took me aside and said, have you ever considered that
the decisions that you don't agree with are the result of information you don't have? And then they took me into a situation where, where I sort of was revealed the, the information I didn't have about the decision I disagreed with was revealed to me. And suddenly I thought it was a great decision. I was like, that's incredible. And then I left and I couldn't talk about it. And I saw other people having the same criticism of the decision. And that complete, that started the process of reformatting how I thought about leadership. Every time I hear a decision now, I think to myself, what do they know that I don't? And that curiosity process is always running. Okay. Lesson you learned the hard way, which is, I feel like this is a very easy question for you, or the misstep that humbled you? There's so much to choose from here. First one that comes to mind. I probably made one on the way here.
I'll pick one that's relevant to the discussion today, which is that I remember distinctly playing in qualifiers in a hacking competition and getting the answer, right, getting the key, right, and running up to the person who was handing in keys for our team. I solved, I don't know what it was, every challenge has a name, right? Like 202. And I'm like, oh, we solved that an hour and a half ago. And I remember, oh, okay, I better find something new to work on. And I just looked around the room, and we're all curled over our hacking. workstations, two monitors, and a keyboard no one would recognize as a keyboard. We all look the same. And thinking to myself, I can quantify the IQ in this room, but I can't look around and
quantify how well we're working together. Right? I don't know how aligned we are in this goal of getting the most points and winning here. And I can't look around and figure out how many people here are on the right challenge, are on a challenge that's already been solved, have the tools they need, would be paired with the right person. And myself and a couple of my colleagues started thinking about, like, what is the right way to create social intelligence in technical teams and hacking teams? And that has stuck with me. I mean, that's been a constant thread is just the abandonment of the hero journey and NetIQ is a way that teams accomplish things. Because you will find people working on challenges to get the key, right, as a metaphor, where the problem's already been solved in any organization that isn't working on its EQ. You'll find it everywhere.
Okay. Okay. Talent or accomplishment. I was going to ask you a bunch more, but we're lightning rounding right now. Talent or accomplishment you're most proud of if given the chance to brag? Bragging is not in my nature. I know, which is the one. Flex a little bit. I taught myself to juggle while my knee was blown out. That's the thing you're most proud of is juggling? Well, so if you haven't learned how to juggle, it's fine, right? But if you have, you know that 99% of it is dropping them and they go everywhere, which when you're immobilized with a busted knee, it's actually harder than it sounds. So I engineered a way to teach myself to juggle where I just got myself into a small enough space that I couldn't lose them. I could just sit there with my blown out post-surgery knee
and teach myself to juggle. I did it in a couple of weeks. Can you still juggle? Oh, yeah. Okay, so if I handed you stuff later. I mean, let's not break the room, but sure. Okay, last one. Career path you would have chosen. This is going to be hard if you weren't in cybersecurity. And it feels like it's in your DNA, so I'm not sure, but I would love to hear an attempt. Oh, it's science fiction writer, 100%. Really? You know, I thought I was going to be a musician, but when you go out and you start getting into a music scene, you kind of find out if you were a natural or not. So I think science fiction writer is still the thing where I wish I'd kept at it a little more. All right, I'm going to break my own rule, which is a social construct, and ask you one more, which is, can you recommend to the audience? a really good, your favorite or one of the best sci-fi books you've ever read? Oh, sure. Easy.
It's the forever war. Haldeman's forever war. And it's, I think it's about coming to hand in the key, except the challenge is already solved, except sort of writ large in a universe governed by relativity. Okay. No spoilers. No spoilers. All right, fine. Thank you so much, Mike. This was a great time for joining me to our audience. Thank you for listening. If you want to learn a little bit more about any of my colleagues in Microsoft Research and their work, check out the Microsoft Research website at aka.ms forward slash research, or listen and watch other episodes of the podcast on YouTube and major podcast platform. Thank you.
番組の概要欄(原文)
Research Manager Mike Walker reflects on a career spanning hacker culture, cybersecurity, and AI, sharing lessons about trust, teamwork, leadership, and why solving difficult problems requires curiosity, judgment, agility—and an understanding of the rules. Show notes
出典・この記事について
- 番組
- Microsoft Research Podcast(Researchers across the Microsoft research community)
- 元の回
- Learn the rules: The hacker mindset
- 配信日
- 要約作成日
- 公式サイト
- podcast.show/microsoftresearch
この要約・解説記事は、元の音声を文字起こしした内容をもとに AI(Claude)が日本語で作成したものです。 固有名詞や数値に誤りを含む場合があるため、正確な内容は元の音声でご確認ください。制作方法について
関連エピソード
AI:AM 週次ハイライト:Arenaのアライメント指数、Kepler の強誘電体メモリ、エージェント経済、AI主導のサイバー攻撃、Mistral Large 4「Le Chonk」
"The Cognitive Revolution"
AIバブルは崩壊するのか?ロバート・ライトのNonzeroとのコラボ回
Doom Debates!
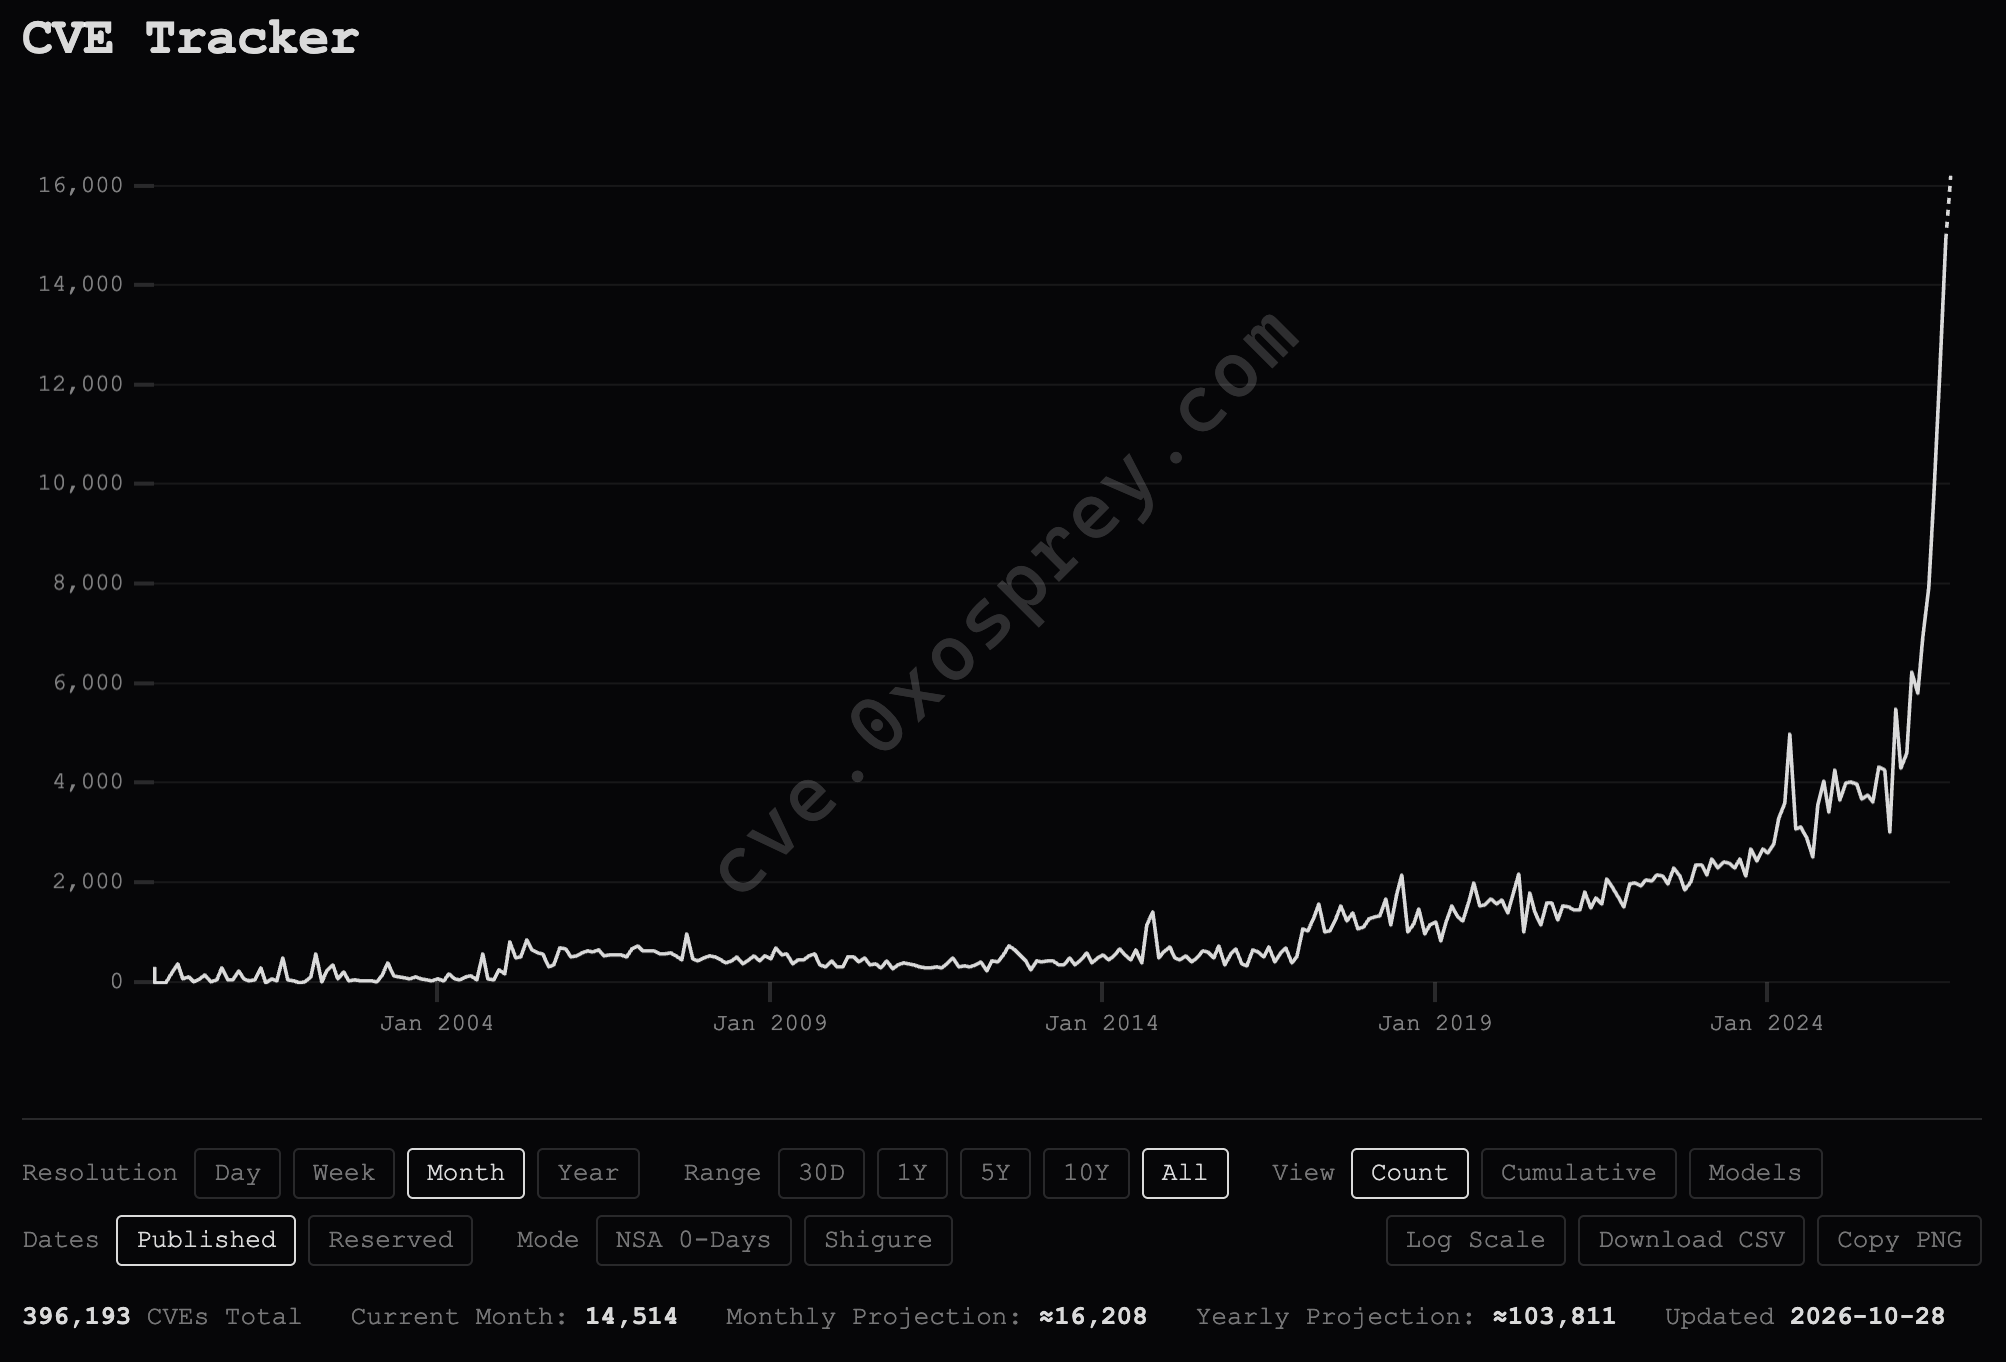
オープンモデルとサイバーリスクについて、私は間違っていたのか?
Interconnects

エージェンティックAI時代のサイバーセキュリティ:Amy Blackshaw(Palo Alto Networks)が語る
Super Data Science: ML & AI Podcast with Jon Krohn

AIバブルかどうか、まもなく分かる――Anthropic IPOとS-1が示すもの
Hard Fork
Microsoft Research Focus 第97号:コーディングエージェントの課題、職場でのAI利用、長期天気予報など
Microsoft Research Podcast